EU’s outsourcing, ICT security guidelines to ‘co-exist’ with DORA

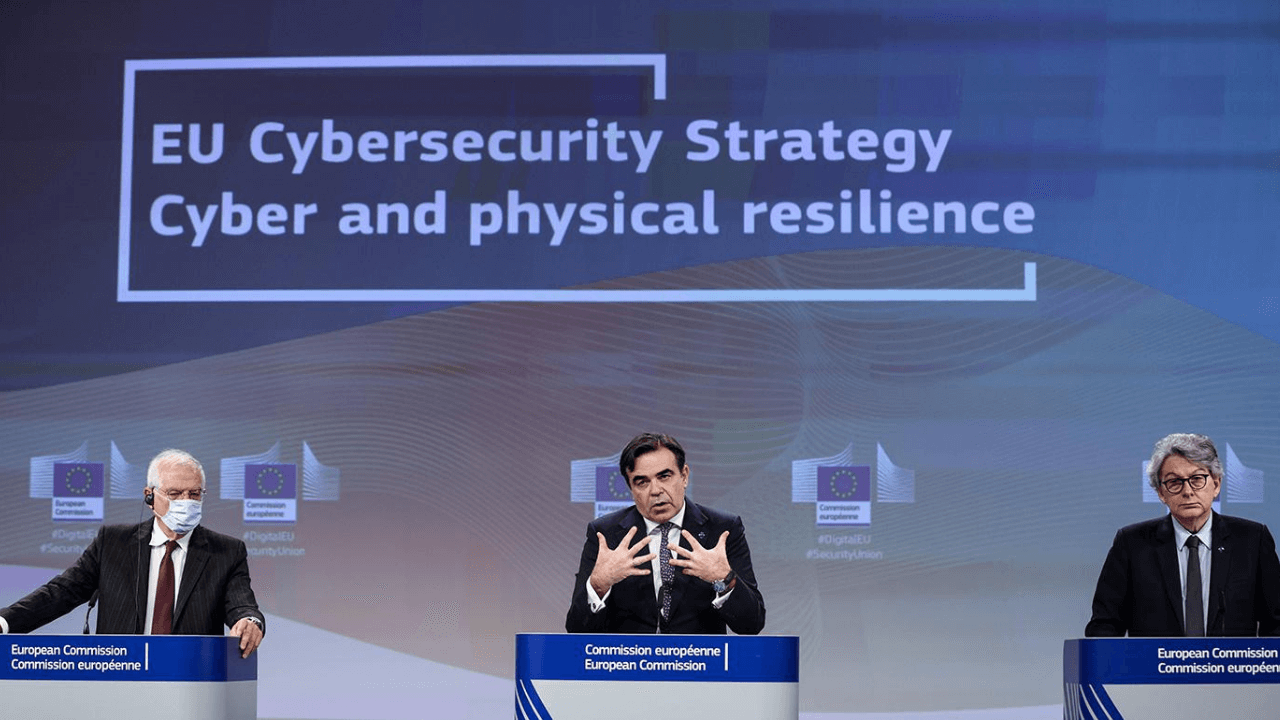
The existing outsourcing and Information and Communications Technology (ICT) security guidelines created by the European Union (EU) will work with the Digital Operational Resilience Act (DORA).
According to a European Commission spokesperson, the guidelines would not be “repealed.” However, they need to amend or delete some parts to reflect DORA’s requirements.
The spokesperson added that DORA will set out “a number of mandates for the three ESAs to develop [regulatory technical standards (RTS) and implementing technical standards (ITS)] which would base the future delegated and implementing acts in the area of ICT risk in finance.”
Several legislation and guidelines reflect the operational resilience requirements in EU financial services. These requirements are set out by different European agencies around outsourcing, using cloud providers specifically, and ICT and security risk management.
DORA aims to set a single set of strengthened, overarching rules for financial entities around ICT risk management.
DORA also envisages direct regulation of significant technology providers to financial entities for the first time, under a framework that would allow ESAs to designate specific ICT third-party service providers as subject to regulation and oversee their compliance.
Related news
- Over 1Mn North Koreans affected by COVID-19 · 17 May
- EU downgrades eurozone growth forecast to 2.7% · 17 May
- South Africa’s BPO sector set for further expansion · 17 May
Disclosure: Outsource Accelerator uses AI tools in the backend of its editorial workflow. Every article is reviewed and verified by a human editor before publication.
Stay ahead of the outsourcing industry. Join thousands of business leaders who rely on Outsource Accelerator for the news, trends, and expert insights that matter. Subscribe to our free newsletter and never miss an update.